when conducting security audits, server location directly affects compliance, forensics, and risk management. this article looks at the pros and cons of setting up this website's server in the united states from a security audit perspective, focusing on the legal, technical and operational aspects to help auditors identify key control points and decision-making factors.
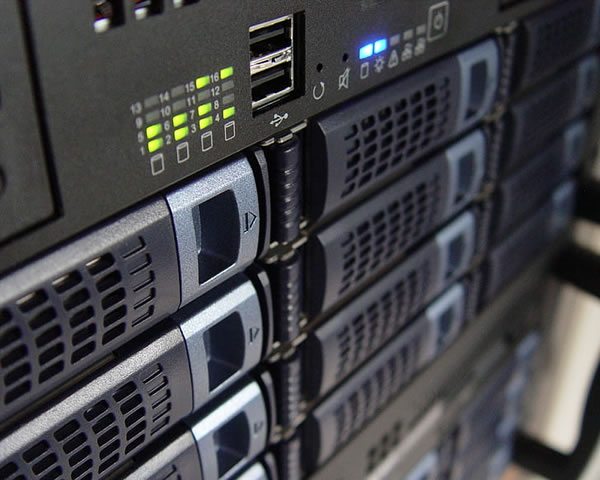
the united states has a mature data center ecosystem, providing complete physical security, power redundancy, and professional operation and maintenance teams. for security audits, clear computer room controls, access logs and third-party security assessment records can improve auditability and event review efficiency.
hosting in the united states is often accompanied by a comprehensive compliance framework and audit support (such as third-party audit reports and security certificates). these materials help prove the implementation of controls during the audit process, facilitate the preparation of audit evidence and continuous improvement of management measures.
when locating servers in the united states, you need to evaluate the impact of local laws on data access. relevant u.s. laws may require cooperation with law enforcement or investigations, and the audit should focus on examining the legal response process, judicial order processing records, and off-site access control.
if a website processes personal data in the eu, domestic or elsewhere, having servers in the united states may raise data sovereignty and cross-border transfer compliance issues. security audits need to check compliance elements such as data classification, transmission encryption, privacy impact assessment and contract terms.
from the perspectives of security and user experience, cross-border hosting may bring network delays and different attack surfaces. audits should focus on edge caching, cdn usage, ddos protection and network segmentation strategies to reduce availability and security risks.
hosting in the united states usually involves third-party cloud or hosting providers. during the audit, the supplier's risks, contractual responsibilities, access rights management and incident response capabilities need to be assessed to ensure that there is a clear communication and evidence collection process in the event of a security incident.
to sum up, setting up servers in the united states has advantages in terms of technology and audit data, but it also brings risks such as legal, data sovereignty and third-party control. it is recommended that security audits include legal compliance assessments, encryption and data minimization principles, clear contracts and response processes, and the trade-off of multi-region or hybrid deployments to balance risk and performance.
- Latest articles
- Popular tags
-
-
Specific Location And Selection Guide For Twitter Servers In The United States
this article will introduce in detail the specific location and selection guide of twitter servers in the united states, helping users better understand twitter’s server architecture and selection criteria. -

Practical Tips For Cost-saving When Cross-border E-commerce Deploys Cera Us High-defense Servers
a practical guide for cross-border e-commerce: when deploying cera high-defense servers in the united states, how to effectively save costs and ensure availability and compliance through architecture, traffic management, cdn and contract negotiation.